A deep dive into the malicious LiteLLM PyPI release - .pth hijacking, layered base64, hybrid crypto exfil, and a dead drop C2 stub.
Posts
2026 — toggle posts for this year
On applying scientific skepticism and rigor to the measurement of agentic security systems.
2024 — toggle posts for this year
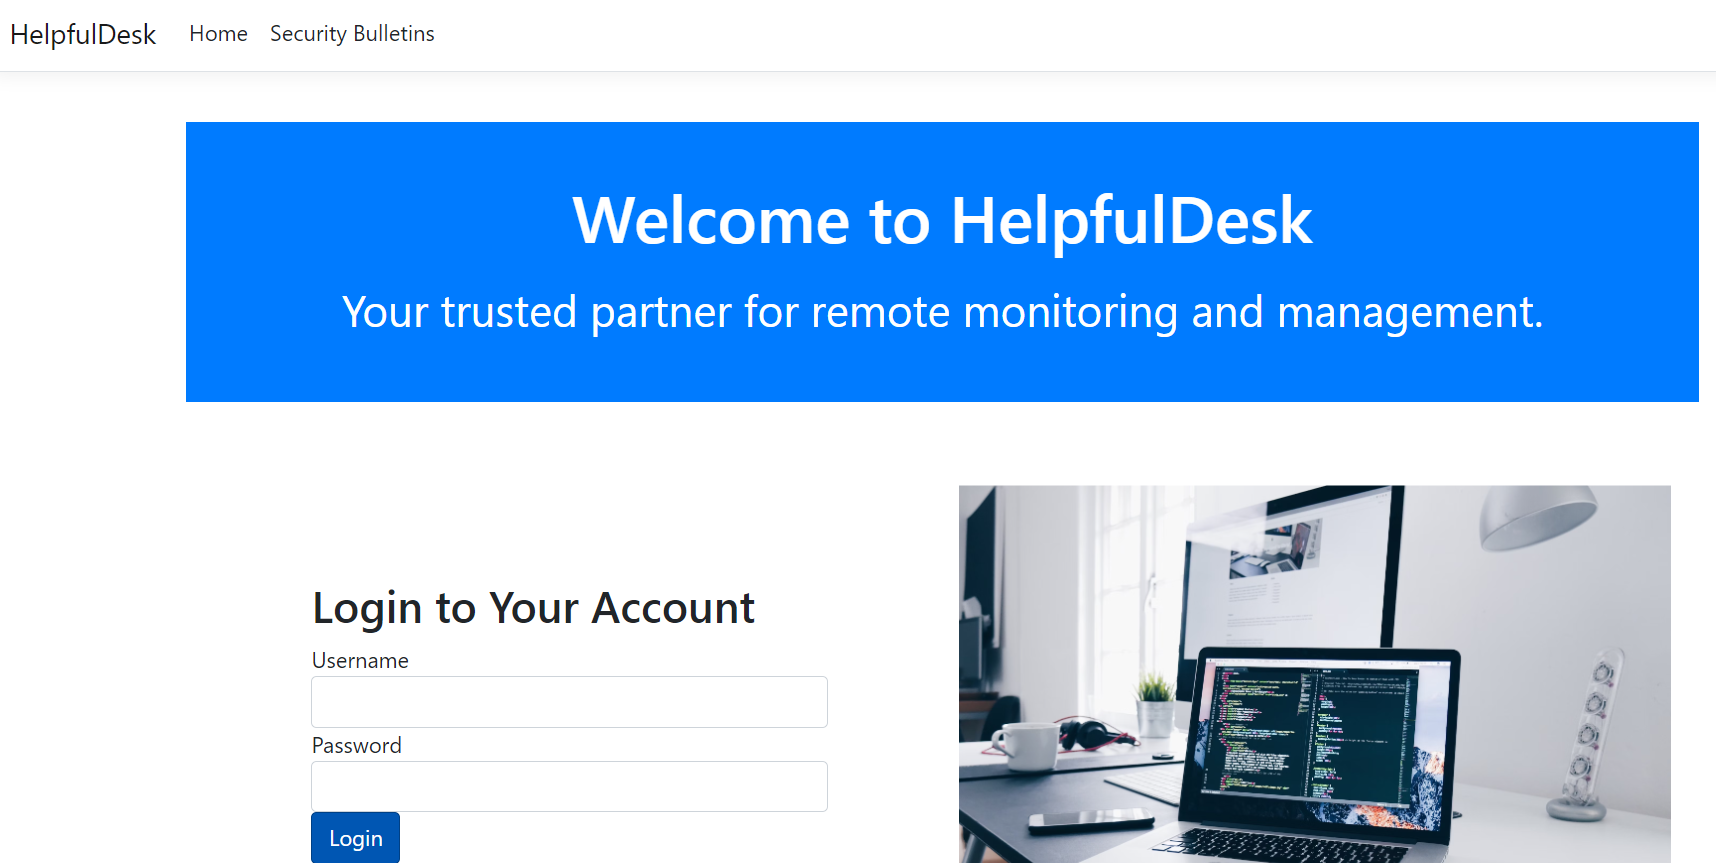
Walkthrough for the HelpfulDesk web challenge from NahamCon 2024 (easy / easy-plus), inspired by the ConnectWise ScreenConnect auth-bypass class of bugs.
2023 — toggle posts for this year
All aboard the hype train! Next stop, JScript Malware Deobfuscation Station! I will waste no time introducing ChatGPT. The technology needs no introduction.…
2022 — toggle posts for this year
This is a free and open section for Practical Malware Analysis & Triage. The full 9+ hour course is available on TCM Security Academy for $29.99. The first 5…
This is a free and open section of Practical Malware Analysis & Triage PMAT , available on TCM Security Academy: Practical Malware Analysis & Triage…
I completed an engagement recently where I designed my threat plan around the recent rash of malicious Windows Installer Microsoft Installer, or MSI programs.…
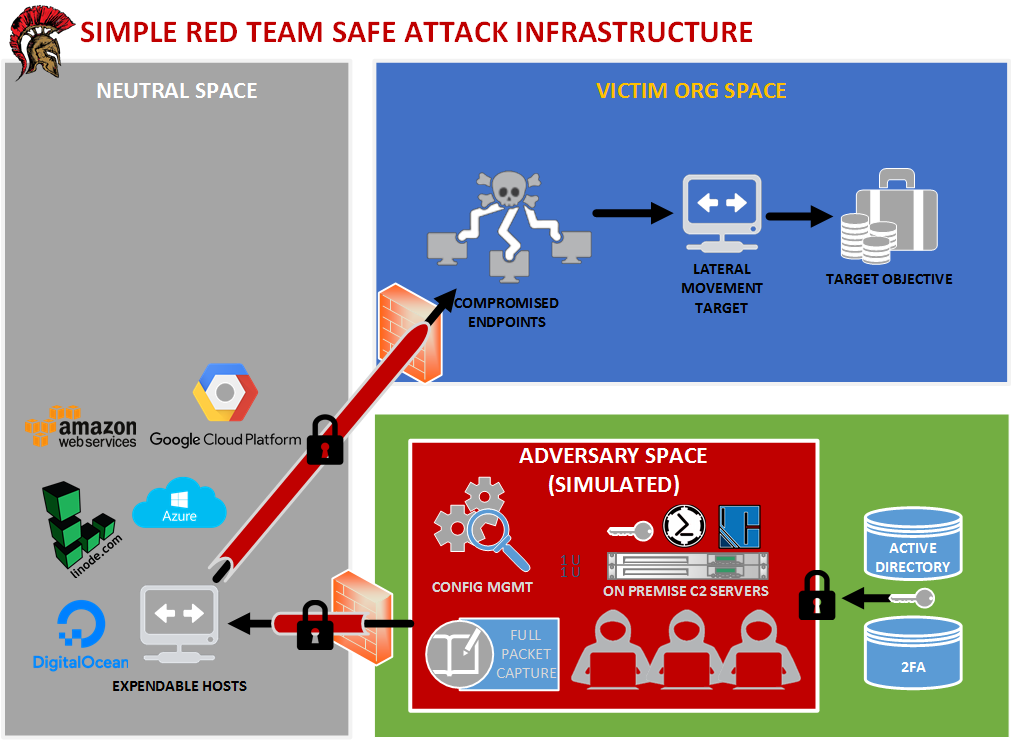
Or at least done safely. 5/18/22 Edit: Hey there! I ended up doing a stream with Taggart on this subject . It was a good time. Check it out here:…
The deep magics of the Component Object Model continually amaze me. Our subject for today’s note post is COM hijacking Adobe Creative Cloud for userland…
I’ve been on a quest to add SCShell https://github.com/Mr-Un1k0d3r/SCShell functionality to OffensiveNotion https://github.com/mttaggart/OffensiveNotion .…
Notion.exe loads quite a few DLLs that are not found in the default install directory of the app itself. It also loads a few that can be outright replaced…
Using the Notion developer API as a C2 platform — co-developed with mttaggart.



2021 — toggle posts for this year
30 minute exploit dev post. Let’s get it.
Want to get into intro level exploit development, but don’t necessarily know where to begin? Read on, fam!
2020 — toggle posts for this year
Maybe some of you reading this would be surprised to find out that I used to be a theater nerd. Actually, I still am one. Even if I haven’t been able…
“A hacking blog bereft of hacking tutorials? What kind of sham site are you running here, Husko?”